A real person, not a black box.
For a lot of small businesses, cyber risk first comes up on an insurance form, with questions about MFA, backups and patching that are hard to answer with confidence when nobody has ever checked.
CertIQ exists to change that. In under 10 seconds it checks what an attacker could see from the outside. Seven plain-English questions take about 90 seconds more, and then it tells you what's fine, what needs fixing and what to fix first. If you want cover, you can request a quote from your report.
CertIQ is run by me, Ben Webster, and I read every message. If something in your report doesn't make sense, or you think I got it wrong, tell me. That's how the product gets better.
About Ben
Ben Webster is the founder of CertIQ. He has spent fifteen years in the Australian and Lloyd's insurance markets as a founder, builder and operator, including founding SanctionsCheck, a sanctions screening service built for insurers and underwriting agencies. His background is in UX, product design and software.
He built CertIQ after seeing the same gap again and again. When cyber insurance comes up, a business is asked about its security and usually has no objective way to answer. CertIQ gives business owners that view first, in plain English.
Ben isn't a security consultant, and CertIQ isn't a penetration test or a formal Essential Eight assessment. It checks what's visible from the outside, asks seven questions, and tells you what to fix first. If a finding looks wrong, he wants to hear about it.
Ben is based in Sydney.
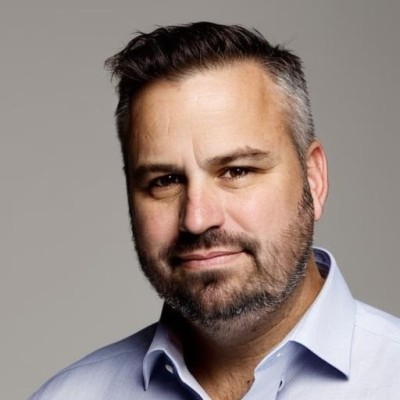
I built CertIQ so any business owner can understand their cyber risk without a consultant. Get in touch. I'd genuinely like to hear from you.
An Australian company